Hub: Access Control Systems Keyword target: configure HID NFC door readers
Configure NFC Door Access Without Credential Failures
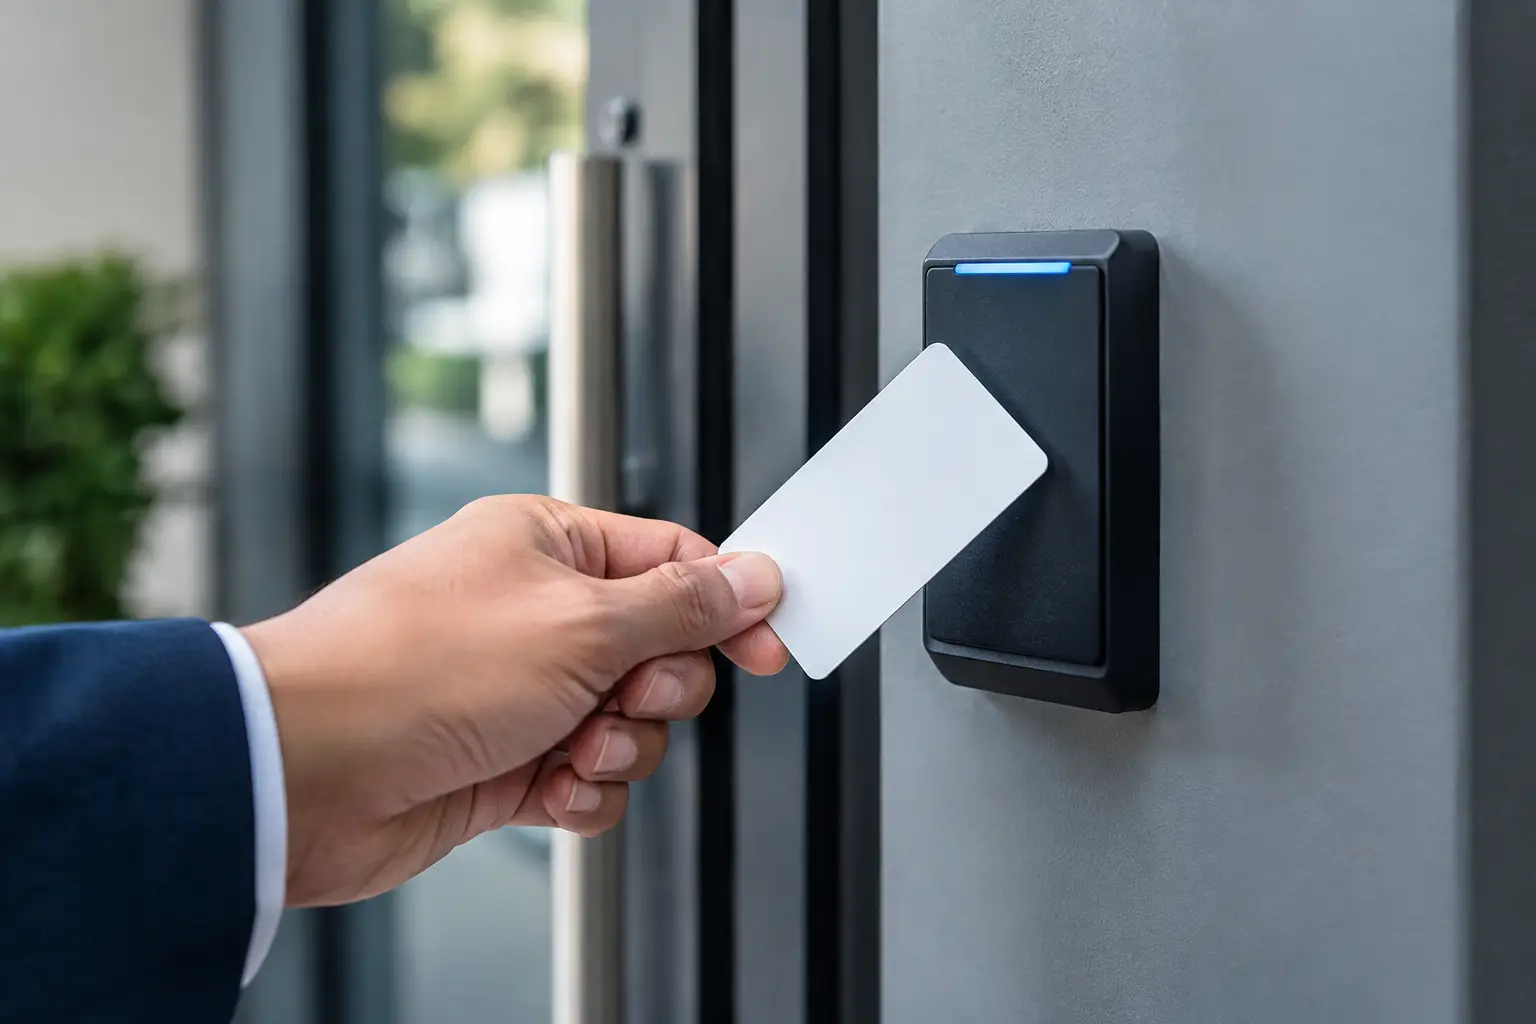
An NFC reader that powers up and beeps is not necessarily ready for a commercial access-control deployment. The difficult work is aligning reader behavior, credential policy, controller communication, and site acceptance requirements before the doors are handed over. When project teams configure HID NFC door readers, the objective is not merely to read a phone or card. It is to produce a controlled, auditable entry point that behaves consistently across every authorized credential.
HID readers are often specified where integrators and consultants need an established access-control platform with a clear migration path from physical cards to mobile credentials. The reader is only one part of that outcome. Its configuration must correspond with the controller, access-control software, credential population, wiring method, and the client’s operational rules.
Start with the access decision, not the reader setting
Before selecting reader modes or loading any configuration, define what the opening event must look like at each door. A staff entrance, secure plant room, government office, and visitor-controlled lobby can each require different credential rules, schedules, door states, and audit expectations.
For NFC access, establish whether the project will use physical cards, mobile credentials, or both. A mixed estate is common during phased upgrades, but it needs deliberate credential policy. The system must identify which formats are accepted at which openings, how lost phones and cards are revoked, and whether a user can hold more than one active credential.
This is also the point to determine whether NFC is intended as a primary access method or one method within a broader credential plan. A reader may support multiple technologies, but enabling every possible format without a defined policy creates avoidable risk. It can complicate troubleshooting, confuse operators, and permit credential types that were never included in the security design.
For consultant-led and tender-driven work, document these decisions in the door schedule and reader configuration record. That record should state the door name, reader location, controller panel, communication method, credential types permitted, lock behavior, request-to-exit arrangement, and any local alarm inputs. It becomes the reference when site teams test a failed transaction later.
Choose the reader-to-controller communication method
Reader communication is a design and commissioning decision, not a wiring afterthought. HID reader deployments may use legacy interfaces or supervised communication protocols, depending on the reader model, controller capability, and project standard. The selected method affects the level of monitoring available between the controller and reader as well as the installation approach.
Where a project is modernizing an existing estate, retaining a legacy interface can simplify a staged replacement. The trade-off is that legacy environments may offer less visibility into reader connection issues. For new builds and higher-security openings, teams commonly evaluate supervised reader communication because it supports stronger device-level control and clearer fault diagnosis when implemented across compatible components.
Do not assume that a reader, controller, and software platform will use the same settings out of the box. Confirm the exact HID reader model, controller firmware, panel interface, and software integration requirements before equipment is released for installation. A mismatch can leave the reader powered but unable to communicate correctly, which is a different fault from a credential rejection.
Cable routing and power allocation also belong in this discussion. Long runs, shared power supplies, poor shielding, and improper grounding can create intermittent behavior that looks like a software problem. The installer should follow the approved wiring documentation for the exact reader and controller combination, while the commissioning team verifies stable communication before loading a full credential database.
Configure HID NFC door readers around credential policy
The reader configuration must reflect the credential policy agreed at the beginning of the project. That includes the technologies enabled, how mobile credentials are presented, any facility-specific identifiers, and reader feedback such as LEDs and audible tones. Feedback is operationally useful: users and security staff should be able to distinguish a valid access decision, denied access, and a door or communications fault without guessing.
Configuration tools and procedures vary by HID reader family and the access-control ecosystem. Some deployments use field configuration through approved mobile or desktop tools, while others rely on configuration managed through the connected system. The correct route depends on the selected reader and the client’s governance requirements. Use only approved configuration methods and maintain a controlled record of the final settings.
For mobile credentials, the reader is not the entire enrollment process. The organization needs a controlled method to issue credentials, associate them with people or roles, deactivate them when access ends, and manage replacement devices. A reader can correctly detect an NFC credential and still deny entry because the credential has not been issued, has expired, lacks door permission, or is not synchronized with the access-control platform.
Avoid treating mobile access as a convenience feature added at the end of the project. It affects security administration, help-desk procedures, visitor workflows, and client training. If the client expects phones to replace cards at certain doors, test that behavior with the actual credential lifecycle process, not with a single demonstration credential.
Keep secure configuration records
Reader configuration should be handled like any other controlled security asset. Restrict configuration access to authorized project personnel, retain approved files or parameter records, and record changes by door and date. Default settings, undocumented technician changes, and shared administrative access make future service difficult and can undermine the original security intent.
The handover package should identify the reader model, installed firmware where relevant, configuration method, enabled credential technologies, controller association, and any site-specific settings. This gives the system integrator and end user a usable baseline for future expansion or incident review.
Test the full door sequence, not only the credential read
A successful credential presentation is only the first test. Acceptance should verify the entire access event from reader presentation through controller decision, lock release, door position change, and transaction recording in the management software.
Test valid and invalid credentials, different authorized user groups, scheduled access conditions, door-held and forced-door alarms where installed, request-to-exit operation, and behavior during a communication interruption. The intended response to controller or network failure should be established by the project security design. It is not a setting to choose casually during site testing.
For NFC credentials, use representative phones and approved credential types rather than relying only on one device used by the commissioning team. Device settings, credential issuance status, user behavior, and operating system differences can affect a real-world trial. The test should prove the defined user journey, including what users see or hear when access is accepted or denied.
When a problem occurs, isolate it in the correct order. First confirm reader power and basic indications. Next confirm reader-to-controller communication. Then verify the controller’s door configuration and the credential record in the management system. Finally, inspect the physical door hardware and lock circuit. This sequence prevents teams from repeatedly reprogramming readers when the actual issue is an authorization rule, wiring fault, or mechanical door condition.
Plan supply and support around the project schedule
Access-control projects rarely fail because a single reader was selected incorrectly. More often, delays arise because reader models, credential types, controller interfaces, and software requirements were not aligned before procurement. For phased sites, standardize the approved reader and credential approach early so future doors do not introduce incompatible configurations.
Seven Sectors Trading Co. supports Saudi Arabian system integrators, consultants, MEP contractors, and procurement teams with HID access-control sourcing for commercial, government, industrial, and infrastructure projects. Share the door schedule, required credential approach, controller environment, and phased rollout requirements before requesting a quotation. This enables the correct reader and supporting components to be specified for the procurement package.
If your project requires HID NFC readers, send the equipment schedule and access-control requirements to info@7sectors.com or submit a Get Quotation form request. A clear configuration plan before equipment reaches site gives the installation and commissioning team a far better starting point than trying to resolve credential policy at the door.
Ready to discuss your project? Contact Seven Sectors or contact us directly on +966-012 229 3474.