A new office tower can have thousands of doors and hundreds of contractors. Its security policy can also change faster than the credential stock in the facilities store. That is why HID mobile versus smart cards is not simply a choice between a phone and a badge. For Saudi commercial, government, industrial, and giga-project access control deployments, it affects several areas. These include reader selection, enrollment workflows, identity governance, operational continuity, and tender compliance.
HID provides both mobile credentials and smart-card technologies within a broader access control ecosystem that includes HID Signo readers. The better option depends on the site, users, installed base, and access control platform administration. In many projects, the right answer is a controlled combination rather than an all-mobile or all-card decision.
HID Mobile Versus Smart Cards: Start With the Operating Model
Smart cards remain the most direct option when a project needs a visible, durable credential. Security teams can issue, collect, and audit it through established security procedures. With a physical HID smart card, guards and facilities teams can immediately confirm that a person holds an authorized credential. It also works for personnel who do not carry corporate smartphones. Similarly, it suits staff who cannot bring phones into secure zones or who work where sites restrict device use.
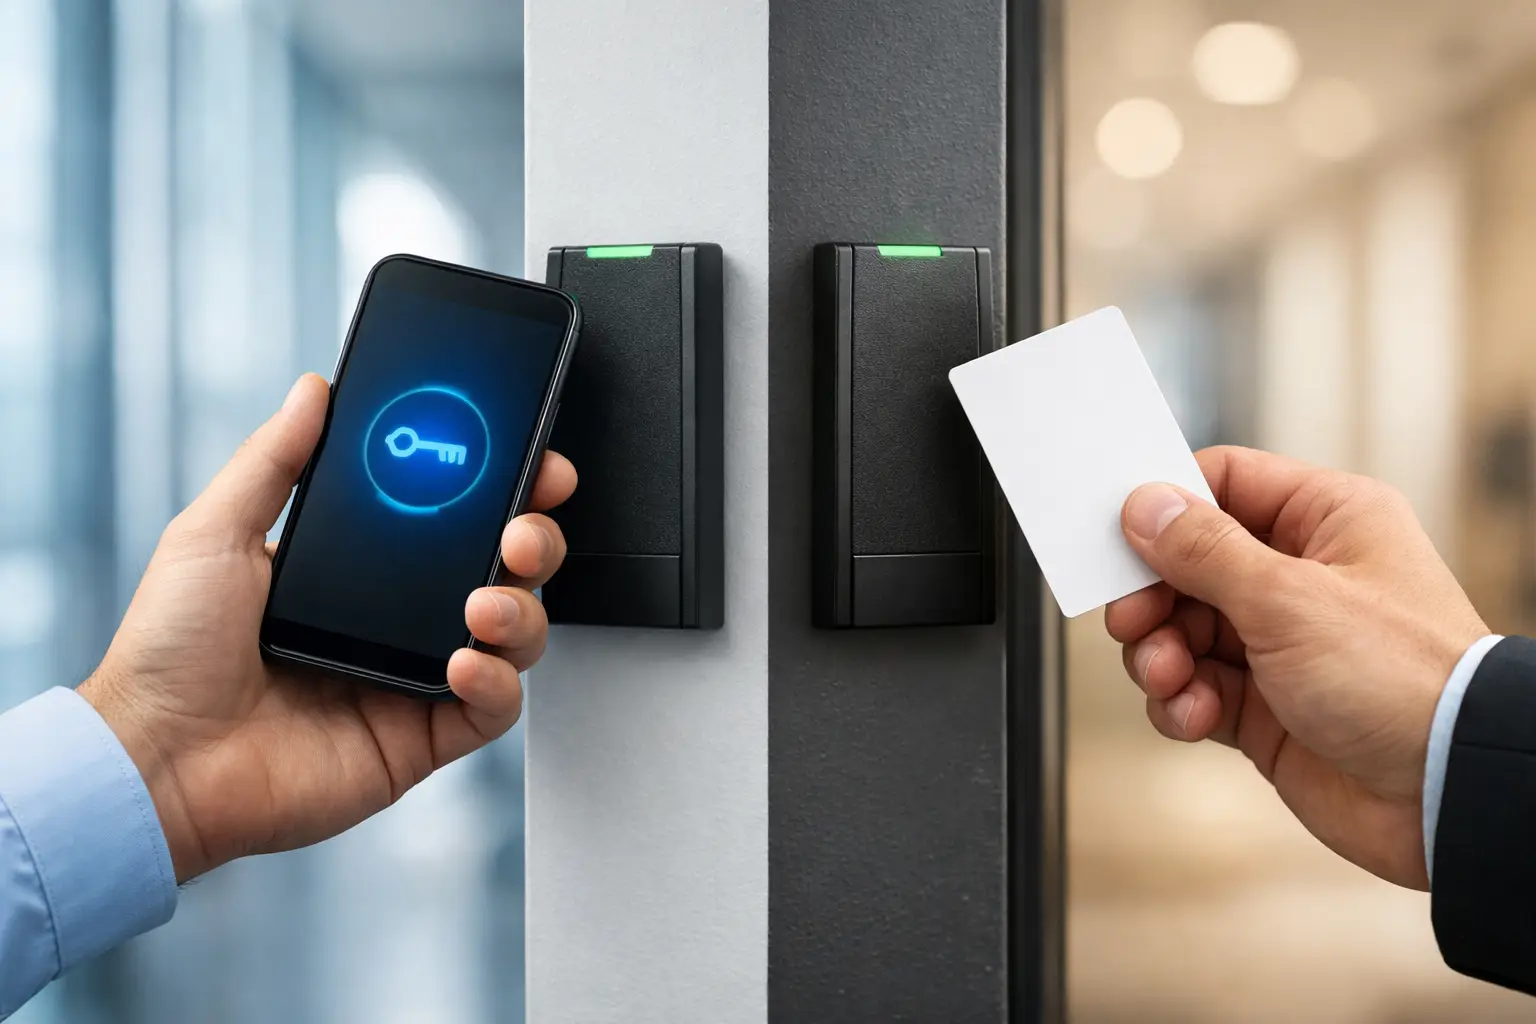
HID mobile credentials replace the physical card with a credential stored on an approved smartphone. A user presents the phone to a compatible reader using Bluetooth Low Energy or NFC. The method depends on the reader, mobile device, and configured mode of operation. This can reduce card handling and allow access teams to issue, suspend, or reissue credentials digitally.
The distinction matters most in workforce-heavy facilities. Consider a headquarters in Riyadh with corporate employees, managed devices, and centralized identity administration. It may gain real operational value from mobile credentials. A logistics operation, refinery support area, construction project, or high-turnover contractor site is different. Such sites may still need smart cards as the primary credential. This is because issuance at the gate is simpler and phone policies differ between employers.
Reader Compatibility Is the First Technical Check
You cannot specify a credential strategy independently from the reader estate. HID Signo readers support modern access technologies, including NFC, Bluetooth, and RFID. However, confirm the exact reader model, configuration, credential technology, controller interface, and licensing before procurement. A reader may support a legacy physical credential. That does not mean it automatically supports every smart-card format or mobile credential workflow the project requires.
For retrofit projects, integrators should document the installed reader population before proposing a transition. This includes reader model numbers, credential formats in circulation, controller capabilities, wiring, and access control software version. The purpose is not only to prevent incompatibility. It is also to identify where the project can phase in mobile credentials. That avoids forcing a costly replacement of every reader at once.
A mixed deployment is often practical. Teams can specify HID Signo readers at executive entrances, tenant floors, staff gates, and visitor-facing areas with high mobile adoption. Meanwhile, smart-card support remains available for operations teams, contractors, and users with no managed mobile device. This avoids turning credential modernization into an exclusion issue.
The communication path from reader to controller also deserves attention. Secure reader-to-controller communication should be part of the design conversation, particularly for government and critical-infrastructure facilities. Moving from an older reader interface to a secure protocol architecture matters for the risk profile. In fact, it may be more significant than choosing a phone over a card. Mobile credentials do not correct weaknesses elsewhere in the access control chain.
Security Is About Credential Lifecycle, Not Just Technology
Both HID smart cards and mobile credentials can support strong access control when teams issue, manage, and revoke them correctly. The weak point is often the process around the credential. Examples include incomplete offboarding, shared cards, and poor enrollment evidence. Another is failure to remove access when a contractor changes role.
Mobile credentials can improve lifecycle control where the organization has a defined identity process. Administrators can provision a credential after HR or sponsor approval. They can then remove it quickly when employment, tenancy, or contract status changes. Users may also benefit from the phone’s own security controls, such as screen lock or biometric authentication. This applies where the device and organizational policy support them.
However, mobile access creates dependencies that procurement teams should acknowledge. The user needs an approved phone, sufficient battery, and a compatible operating system. They also need a support route when a device is lost, replaced, or unavailable. In restricted facilities, the organization may prohibit mobile phones beyond a perimeter. A physical smart card then becomes mandatory, even if the rest of the campus uses mobile credentials.
Smart cards have a different operational risk profile. People can lose or loan them. Someone can copy them if the site retains obsolete technology. They can also stay active after the holder leaves. Those risks are manageable through strong enrollment, card return procedures, credential audits, and modern secure smart-card technology. Old low-frequency proximity cards and modern contactless smart cards are both physical badges. However, a project should not treat them as equivalent.
Cost Must Be Measured Across the Credential Lifecycle
The initial unit cost of a card versus a mobile credential is only one line in the project budget. Smart cards require stock management, printing where sites need visual identification, issuance stations, replacements, and periodic reorders. For large organizations with frequent staff movement, those administration costs can be material.
Mobile credentials can reduce dependence on physical card inventory, but they introduce other commercial considerations. The project may require compatible HID Signo readers and credential subscriptions or platform entitlements. It may also need user support procedures and coordination with corporate mobility policies. The financial case becomes stronger when the organization can use its existing identity governance and mobile-device management processes. This avoids creating separate manual workflows.
For tender evaluation, compare the five-year operating model rather than the first purchase order. Include replacement rates, credential issuance labor, reader upgrades, software requirements, and visitor and contractor volumes. Also include the cost of maintaining dual credential types during migration. A mobile-first strategy with no provision for exceptions can create avoidable delays at site access points.
Government and Giga-Project Procurement Considerations
Saudi government and Vision 2030 project procurement often includes strict requirements for approved supply chains, documentation, cybersecurity, and product origin. Some projects require NDAA or TAA compliance. In that case, review it against the specific product, part number, project requirement, and applicable procurement terms. Selecting a mobile credential or smart card does not by itself establish NDAA or TAA compliance.
Consultants should request clear manufacturer documentation for everything in the bill of materials. That includes the HID readers, credentials, software components, and interfaces. They should also define credential ownership and administration responsibilities. This is particularly relevant where several parties approve access. A master developer, operator, security contractor, and tenant organization may each have different roles.
For multi-site developments in NEOM, Riyadh, Jeddah, or the Eastern Province, a consistent credential standard can simplify operations. Yet consistency should not mean forcing one credential method on every user group. For example, field teams can use a secure smart card while office users carry a HID mobile credential. Both can operate under the same access policy while respecting different site conditions.
When Smart Cards Are the Better HID Choice
HID smart cards are usually the stronger starting point where personnel must display visual ID or the site prohibits phones. The same applies where workforce turnover is high or teams must issue credentials immediately at a controlled enrollment desk. They also suit facilities that need dependable access for users who may not have managed smartphones or consistent access to mobile support.
They are especially effective when a project needs to retain a familiar gate-entry process. This holds true while the site improves credential security from an older proximity-card environment. The priority is to specify the appropriate HID smart-card technology and compatible readers. Do not assume every card provides the same level of protection.
When HID Mobile Credentials Make More Sense
HID mobile credentials are a strong fit for corporate campuses, premium commercial assets, and higher-education environments. They also suit organizations with mature HR, IT, and identity workflows. They can improve convenience for regular users while reducing the cycle of printing and replacing staff badges.
When projects select compatible HID Signo readers, mobile credentials also support a more flexible access experience. This applies at common entrances, parking areas, and shared facilities. However, the project should maintain an exception policy for device loss, depleted batteries, and temporary staff. The policy should also cover users who cannot use a personal or corporate smartphone for access.
Specify for Choice, Then Govern the Exception
The most resilient HID strategy is often one that supports both mobile credentials and secure smart cards from day one. This gives the operator a controlled migration path and protects access continuity. It also avoids imposing a single user policy on every building function.
Seven Sectors supports system integrators, consultants, and procurement teams sourcing HID access control products for Saudi projects. Do you need HID Signo reader, mobile credential, or smart-card availability? Contact Seven Sectors at info@7sectors.com or submit the website Get Quotation form for pricing and availability.
Frequently Asked Questions
What is the difference between HID mobile credentials and HID smart cards?
HID mobile credentials are stored on a smartphone and presented to HID Signo readers via NFC or Bluetooth, eliminating the physical card. HID smart cards (iCLASS SE, SEOS, DESFire) are physical credentials carried in a wallet or on a lanyard. Mobile credentials offer faster provisioning and remote revocation; smart cards are preferred where staff have no issued smartphone, where security policy prohibits personal devices at readers, or where the environment is incompatible with Bluetooth.
Can HID mobile and smart-card credentials work on the same reader and site?
Yes. HID Signo readers support multiple credential technologies simultaneously — NFC mobile, Bluetooth mobile, iCLASS SE, SEOS, and legacy RFID — on the same reader. A single site can issue smart cards to operational staff, mobile credentials to management, and still read both at every door without changing reader hardware. This makes a hybrid deployment practical for Saudi projects with mixed user populations.
Are HID mobile credentials suitable for Saudi government facilities?
HID mobile credentials via HID Origo Mobile Identities platform provide enterprise-grade security including encryption and remote revocation. Suitability for a government facility depends on the facility’s security policy regarding mobile devices in secure areas. Many government clients operate a hybrid model: mobile for low-security zones, smart cards for controlled-access areas. Seven Sectors can advise on credential strategy for your project.
How are HID mobile credentials enrolled and revoked for Saudi projects?
HID mobile credentials are managed through HID Origo, a cloud-based identity platform. Administrators invite users via email or API, users download HID Mobile Access to their device, and credentials are provisioned remotely. Revocation is immediate and does not require physical card collection. For large Saudi projects, Seven Sectors can guide integrators on enrollment workflow design and system integration.
Ready to discuss your project? Contact Seven Sectors or contact us directly on +966-012 229 3474.